Understanding Mastercard’s New Scam Monitoring Requirements

Understanding Mastercard’s New Scam
Monitoring Requirements

As fraud and scam activity continue to evolve across the payments ecosystem, Mastercard is introducing enhanced monitoring standards designed to help identify and prevent scam-related merchant activity before it can cause significant harm to consumers, issuers, and the payments industry.

Effective July 24, 2026, Mastercard will require acquiring banks, payment processors, and payment facilitators to implement additional monitoring and investigation procedures for merchants that exhibit characteristics commonly associated with scam activity.

The payments industry has experienced a growing number of scams that can be difficult to detect through traditional fraud monitoring methods. While many businesses operate responsibly, scammers often use legitimate-looking websites, advertisements, and payment acceptance channels to deceive consumers.

Mastercard’s revised standards are intended to strengthen oversight, improve consumer protection, and ensure that acquiring institutions can quickly identify potentially harmful activity before it impacts larger numbers of cardholders.

A scam merchant is generally a business that uses deceptive practices to persuade consumers to make purchases, subscriptions, investments, or other payments under false or misleading circumstances.

Examples may include:

  • Misleading subscription offers
  • Investment or cryptocurrency scams
  • Fake product or service websites
  • Deceptive trial offers
  • Businesses using false advertising or misrepresentation to obtain payments

The new standards focus on identifying unusual transaction behavior that may indicate these types of activities.

Mastercard already requires ongoing merchant monitoring, but the revised standards introduce additional triggers that may require a formal investigation.

Some examples include:

  • Sudden increases in chargebacks or refund activity
  • Significant drops in authorization approval rates
  • Reports from card issuers indicating potential scam activity
  • Alerts from approved monitoring services
  • Transaction activity that appears inconsistent with the merchant’s stated business model

For newly boarded merchants, special attention will be given to refund and chargeback activity during the first six months of processing.

For legitimate businesses, these changes should have minimal operational impact.

However, merchants should be prepared to provide additional information if unusual activity is detected. This may include:

  • Clarification regarding business practices
  • Marketing materials and advertisements
  • Customer service procedures
  • Refund policies
  • Evidence supporting product or service delivery

Maintaining transparent business practices and responding promptly to information requests can help avoid unnecessary disruptions.

To minimize risk and maintain a healthy processing relationship, merchants should:

  • Clearly disclose products, pricing, and subscription terms
  • Maintain responsive customer service channels
  • Process refunds promptly when appropriate
  • Monitor chargeback activity closely
  • Ensure advertising accurately reflects products and services offered
  • Review website disclosures and terms regularly

Merchants with strong operational controls and transparent customer communications are generally far less likely to encounter issues under Mastercard’s monitoring programs.

At Viking, we continuously monitor regulatory and card brand developments to help protect both our merchants and sponsoring financial institutions.

Our compliance, underwriting, and risk teams work closely with merchants to identify potential concerns early, provide guidance when needed, and ensure that businesses remain aligned with Mastercard and Visa requirements.

These new standards represent another step toward creating a safer and more trustworthy payments ecosystem for merchants, consumers, processors, and financial institutions alike.

If you have questions regarding Mastercard’s revised scam merchant monitoring requirements or how they may impact your business, please contact your Viking representative today.entation, our team is ready to assist. reach out to your Viking representative today.

June 2, 2026

About Robert Hollifield

He is an accomplished director with 15 years of experience in underwriting, risk management, and compliance in the payments space. He specializes in high-risk merchant oversight, regulatory adherence, and improving end-to-end payment processes to ensure secure, reliable operations. He received his BS from the University of New Hampshire.

Bigger Possibilities Await.

Contact Us


Read More

Same Day ACH Tops $1.1 Trillion: What Record Growth Means for Lenders

Same Day ACH Tops $1.1 Trillion

What the Latest Growth Mean for Lenders

Borrowers have become accustomed to instant access. They can order products online, transfer money between accounts, and receive payments within seconds. As these expectations continue to shape consumer behavior, they are increasingly influencing the lending industry as well.

When a loan is approved, borrowers no longer compare their experience solely against other lenders. They compare it against every other digital experience in their lives. Waiting days for funds to arrive can feel outdated, particularly when the need for funds is urgent.

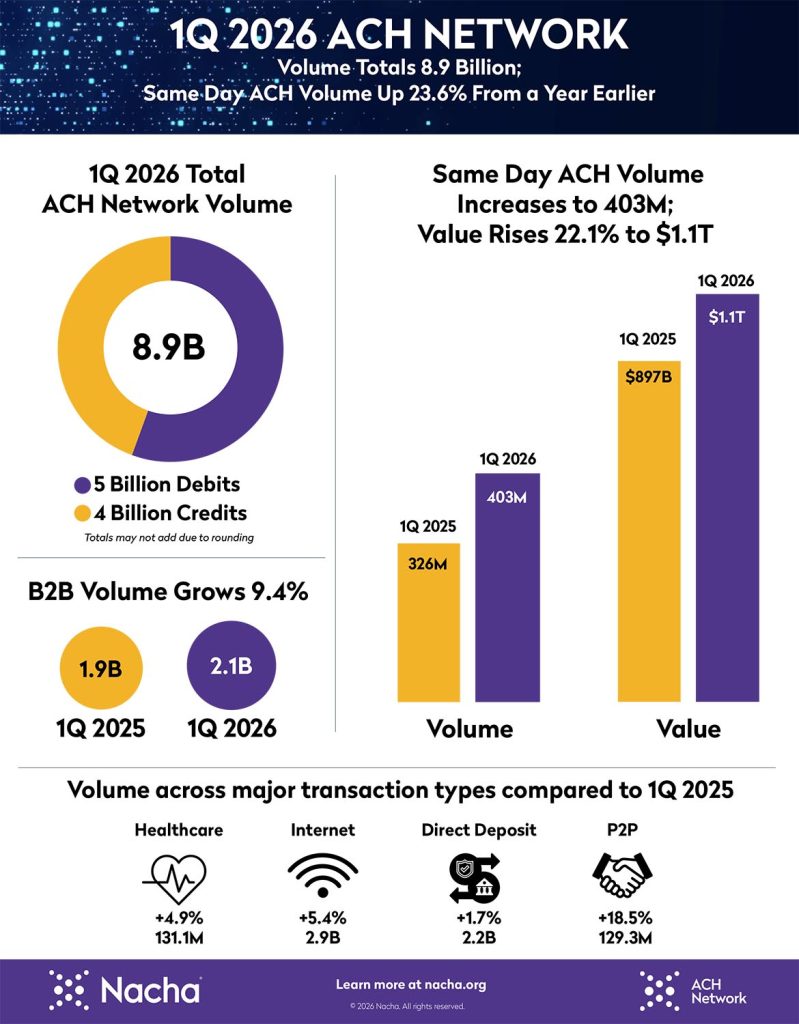
Recent ACH Network growth data suggests that financial institutions and businesses are responding to this demand for faster payments. During the first quarter of 2026, Same Day ACH volume increased 23.6% year-over-year to 403 million payments, while the value of those payments reached $1.1 trillion, an increase of 22.1%.

These numbers demonstrate that faster payment capabilities are becoming increasingly important across the financial ecosystem, including lending.

Same Day ACH volume reached 403 million payments during the first quarter of 2026, while payment value exceeded $1.1 trillion for the second consecutive quarter.

For many borrowers, access to funds is the most important part of the lending experience.

A streamlined application process and quick approval lose much of their value if borrowers must wait days to receive their money. Whether funding is needed for emergency expenses, home repairs, vehicle repairs, medical bills, or short-term cash flow needs, delays can negatively impact borrower satisfaction.

Faster funding can help lenders:

  • Improve borrower satisfaction
  • Increase repeat borrowing activity
  • Strengthen customer retention
  • Differentiate themselves in a competitive market
  • Reduce funding-related support inquiries

As borrower expectations continue to evolve, funding speed has become an important part of the overall customer experience.

While much attention has been focused on real-time payment networks such as RTP and FedNow, Same Day ACH continues to experience significant growth.

One reason is accessibility.

Most financial institutions already participate in the ACH Network, making Same Day ACH a practical option for many lenders that want to accelerate funding without implementing entirely new payment workflows.

Same Day ACH can help lenders:

  • Deliver funds faster than traditional ACH
  • Improve operational efficiency
  • Reduce delays caused by batch processing
  • Provide more predictable settlement timing
  • Expand funding options for borrowers

For many lending organizations, Same Day ACH serves as an effective bridge between traditional ACH processing and real-time payment solutions.

The first-quarter ACH data also showed strong growth in business-to-business payments and continued expansion across internet-based transactions.

This broader growth reflects an ongoing migration away from paper-based payment methods and toward digital payment experiences.

For lenders, this trend extends beyond loan funding. ACH remains a critical tool for:

  • Recurring loan payments
  • Account verification processes
  • Consumer disbursements
  • Collections and repayment programs
  • Settlement and reconciliation operations

As lending becomes increasingly digital, ACH continues to provide the foundation for many borrower-facing payment experiences.

The continued growth of Same Day ACH provides an opportunity for lenders to evaluate whether their payment strategy aligns with borrower expectations.

Consider the following questions:

  • How quickly can borrowers receive funds after approval?
  • Are funding delays creating friction in the borrower experience?
  • Could Same Day ACH improve customer satisfaction or retention?
  • Are there opportunities to incorporate RTP or FedNow alongside existing ACH processes?

Lenders that proactively evaluate their payment capabilities today will be better positioned to meet the expectations of tomorrow’s borrowers.

The first quarter of 2026 highlighted the continued strength of the ACH Network, but the most significant takeaway for lenders may be the ongoing growth of Same Day ACH.

As borrowers increasingly expect faster access to funds, lenders must balance speed, efficiency, risk management, and operational simplicity. Same Day ACH continues to provide a practical solution that helps bridge those competing priorities.

At Viking, solutions such as VIKExpress, VIKEdge, and VIKEngage help lenders modernize payment operations, improve funding experiences, and maintain visibility into transaction performance as payment expectations continue to evolve.

May 7, 2026

About John O’Shea

He is a former founder and owner of Triad Financial Services and has served in similar roles at GMAC/Residential Funding, AllianceOne and ICT Group (now Sykes). He has performed for 28 years as a senior executive in the ARM, Customer Contact and BPO markets. He is a graduate of St. Olaf College.

Bigger Possibilities Await.

Contact Us


Read More

PCI DSS 4.0 in 2025

What Merchants Need to Know
About PCI DSS 4.0 in 2025

If your business accepts credit or debit cards, PCI compliance is essential. The latest version of the Payment Card Industry Data Security Standard, PCI DSS 4.0, is now fully in effect. It introduces major changes designed to strengthen cardholder data protection and adapt to today’s complex digital payment landscape.

This version replaces the older 3.2.1 standard and includes critical enhancements for fraud prevention, authentication, and risk management. Here’s what you need to know and how to stay current in 2025.

PCI DSS 4.0 is the global security standard for any organization that stores, processes, or transmits cardholder data. It was officially released in March 2022 and became the mandatory standard as of March 31, 2024. A clarification update, version 4.0.1, was published in mid-2024 to refine language and improve implementation guidance without changing the core requirements.

The real shift came in April 2025, when many of the formerly “best practice” or future-dated requirements became enforceable. Merchants must now fully align with PCI DSS 4.0 and address all applicable requirements, including those phased in over the past year.

April 1, 2025, marked the date when PCI DSS 4.0 enforcement began in full. Businesses that have not transitioned from 3.2.1 risk fines, higher merchant fees, breach liability, and potential disruption of card processing services.

The update reflects the growing complexity of modern payments, where merchants may process card data across physical points of sale, mobile apps, e-commerce platforms, and cloud environments. PCI DSS 4.0 provides a more flexible framework while raising the bar for security, accountability, and risk management.

  1. Scope Definition and Maintenance
    Merchants must define and document their PCI scope annually. For service providers, this must be done every six months. This includes identifying all systems and components involved in storing, processing, or transmitting cardholder data.
  2. Multi-Factor Authentication (MFA)
    MFA is now required for all access to the cardholder data environment, both internal and external. This eliminates prior exemptions and greatly improves protection against unauthorized access.
  3. Stronger Password Controls
    User passwords must now be at least 12 characters long unless a system limitation exists. This aligns PCI DSS with modern password standards for increased security.
  4. Web Application Security
    Public-facing payment pages must use a web application firewall or equivalent controls. Merchants must also monitor the integrity of all scripts loaded into these pages to prevent tampering or injection attacks.
  5. Automated Logging and Monitoring
    Merchants must implement automated logging systems to detect and alert on failures in critical security controls. Manual log reviews are no longer sufficient.
  6. Vulnerability Management and Software Inventory
    All internal vulnerability scans must be authenticated. Merchants must also maintain an inventory of software components using a Software Bill of Materials (SBOM) to quickly address known vulnerabilities.
  7. Phishing Defense and Awareness
    Anti-phishing technologies and employee training are required. This includes protecting users from fraudulent emails that could lead to credential theft or unauthorized access.
  8. Incident Response and Data Discovery
    Incident response plans must now include procedures for detecting unauthorized storage of cardholder data, not just responding to breaches.

While the 4.0 standard is stable, version 4.0.1 introduced clarification on several areas including encryption expectations, hashing, and vendor responsibilities. The PCI Council emphasized the importance of maintaining SBOMs and reinforced that organizations should now be implementing customized approaches only when clearly documented and reviewed.

Key reminders from recent updates include:

  • Use of keyed hashing algorithms
  • Proper encryption key lifecycle management
  • Annual scope validation
  • Documented roles for shared responsibility with third-party vendors

If your business is still catching up with PCI DSS 4.0 requirements, here are key action items to prioritize:

  • Perform a gap analysis against current operations and 4.0 requirements
  • Implement MFA for all users accessing systems in scope
  • Deploy or validate use of web application firewalls
  • Set up automated logging and alerting tools
  • Complete an SBOM for all software in your cardholder environment
  • Train staff annually on security awareness, phishing, and incident response
  • Confirm your third-party service providers are PCI compliant and responsibilities are clearly defined

Compliance is not just a technical checklist. PCI DSS 4.0 is about protecting your customers, your reputation, and your financial stability. Data breaches can be devastating, both in terms of brand damage and regulatory penalties. By staying compliant, you reduce risk, maintain trust, and avoid potential disruptions to your ability to process payments.

At Viking, we offer platforms and services built with compliance in mind. Whether you’re using VIKExpress for card-not-present transactions, VIKEdge for ACH with bank balance verification, or VIKEngage for transaction monitoring, we make sure your payments are processed securely and responsibly.

We can also help with:

  • PCI compliance assessments
  • Policy and documentation support
  • Vendor responsibility checklists
  • Technical integrations for MFA, logging, and scanning
  • Ongoing training and incident response planning

If you’re unsure whether you’re ready for PCI DSS 4.0.1 or need help getting your systems in line with the new standards, reach out to your Viking representative today.

Let’s make sure your payment security is not just compliant, but resilient.

June 7, 2025

About Thomas Stephens

He is a skilled professional in payment operations and technical support, with deep expertise in payment technologies, enhanced workflows, and leading end-to-end system and platform integrations. He brings over 10 years of experience ensuring reliable, secure payment solutions while driving process improvements and delivering high-level support across fast-paced environments. 

Bigger Possibilities Await.

Contact Us


Read More

Upcoming NACHA Rules Changes: Implications for Originators and Merchants

Upcoming NACHA Rules Changes

Implications for Originators and Merchants

As a payment compliance specialist, it is critical to stay abreast of the latest NACHA (National Automated Clearing House Association) rule changes. Two sets of amendments are set to take effect this year—on June 21 and October 1, 2024. Some of these changes will impact originators and merchants significantly, emphasizing the need for proactive adjustments to compliance and operational strategies.

June 21, 2024: Minor Rules Topics

The first wave of changes focuses on minor rule topics. Minor changes to the Rule have little to no impact on ACH participants and no significant processing financial impact.

  1. General Rule /Definition of WEB Entries– The updated NACHA rule clarifies the use of WEB entries, which are transactions initiated by a consumer over the internet or a wireless network. The new definition eliminates confusion by specifying that all consumer-to-consumer credits must use the WEB SEC code, regardless of the internet or wireless network being the method of initiation.
  2. Definition of Originator– The updated rule provides a clearer definition of an Originator, stating that it is the party authorized by the Receiver to credit or debit the Receiver’s account at the RDFI (Receiving Depository Financial Institution). This clarification helps in precisely identifying the responsible entity in a transaction, thus reducing ambiguities and potential disputes between parties involved in ACH transactions
  3. Originator Action on Notice of Change– This rule requires Originators to take prompt action upon receiving a Notice of Change (NOC) from the RDFI. The NOC indicates necessary corrections to the information within an ACH entry. Originators must make the specified changes within six banking days or before the next entry, whichever is later.
  4. Data Security Requirements– The updated rule extends the data security requirements to all non-consumer Originators, Third-Party Service Providers, and Third-Party Senders.
  5. Use of Prenotification Entries– The revised rule on prenotification entries provides clarity on their use and the handling of responses from RDFIs. Prenotification entries are optional but recommended for verifying account information before initiating live transactions. Originators can use these entries to ensure that account details are correct, reducing the risk of errors and rejected transactions. If an RDFI responds to a prenotification with a NOC, the Originator must address the indicated issues promptly
  6. Clarification of Terminology – Subsequent Entries– The rule clarifies the term “Subsequent Entries,” referring to entries that follow an initial authorization. These can be initiated by the consumer through actions such as phone calls or online requests. The updated rule allows greater flexibility in the use of Standard Entry Class (SEC) codes for these subsequent entries, accommodating various methods of initiation and ensuring that authorization requirements are met appropriately

October 1, 2024: Risk Management Topics

The second set of changes, effective October 1, centers around risk management, reflecting NACHA’s ongoing efforts to enhance the security and reliability of the ACH Network:

  1. Codifying Expanded Use of Return Reason Code R17– The updated rule codifies the expanded use of Return Reason Code R17 to enhance the identification and management of fraudulent activities. This rule includes the following specifics:
    • R17 + “QUESTIONABLE”: The addition of the word “QUESTIONABLE” in the return addenda record signifies a potential fraud alert on the receiving bank account. This helps financial institutions quickly identify transactions that may require further scrutiny for fraud
    • Impact on Unauthorized Return Rates: These returns will not be counted in unauthorized return rates, thus not affecting the metrics used to evaluate the frequency of unauthorized transactions
    • This new Rule also includes references to a newly defined term, False Pretenses: The inducement of a payment by a Person misrepresenting (a) that Person’s identity, (b) that Person’s association with or authority to act on behalf of another Person, or (c) the ownership of an account to be credited.”
      This definition covers common fraud scenarios such as Business Email Compromise (BEC), vendor impersonation, payroll impersonation, and other payee impersonations, and complements language on “unauthorized credits” (account takeover scenario). It does not cover scams involving fake, non-existent or poor-quality goods or services.
    • Expanded Use of ODFI Request for Return/R06–This rule expands the circumstances under which an Originating Depository Financial Institution (ODFI) can request a return of an entry using Return Reason Code R06 (Return per ODFI’s Request). This expansion aims to provide more flexibility and tools for ODFIs to manage erroneous or problematic entries, ensuring better correction of mistakes and reducing potential risks associated with such entries
    • Ensure your loan management and payment processing systems are updated for NACHA’s new R17 rule. This rule allows RDFIs to use Return Reason Code R17 with the descriptor “QUESTIONABLE” in the Addenda Information field to flag transactions that may be suspicious or fraudulent. Updating your systems will help differentiate these returns from routine account errors and maintain compliance with NACHA’s standards.
  2. Additional Funds Availability Exceptions– The rule introduces new exceptions to the funds availability requirements, allowing RDFIs more time to investigate suspicious transactions before making funds available to the account holder. This extension is critical in scenarios where there is a high likelihood of fraud, enabling RDFIs to ensure that the transaction is legitimate before releasing the funds. This change aims to reduce the risk of fraudulent withdrawals and losses for both the financial institution and the account holder
  3. Timing of Written Statement of Unauthorized Debit (WSUD)– The rule modification allows for greater flexibility in the timing of signing a WSUD. Specifically, it permits the WSUD to be signed and dated by the Receiver on or after the date the unauthorized debit entry is presented, even if the debit has not yet posted to the account. This change simplifies the process for receivers to dispute unauthorized debits and facilitates quicker resolution of such issues​
  4. RDFI Must Promptly Return Unauthorized Debit– This rule mandates that Receiving Depository Financial Institutions (RDFIs) must promptly return any unauthorized debit entries once they are identified. This requirement ensures that unauthorized debits are addressed quickly, minimizing the impact on the account holder and reducing the potential for further fraudulent activity. It emphasizes the responsibility of RDFIs to act swiftly in protecting their customers’ accounts from unauthorized transactions

For further details on these rule changes, visit NACHA’s official website on minor rules topics and risk management topics.

Preparing for Compliance

For originators and merchants, preparation is key to ensuring compliance with these new rules:

  • Review and Update Systems: Ensure that all payment processing systems are updated to align with the new data specifications and validation requirements.
  • Train Staff: Conduct comprehensive training sessions for relevant staff to familiarize them with the new rules and their implications.
  • Enhance Fraud Detection: Invest in advanced fraud detection and prevention technologies to meet the updated standards.
  • Audit Third-Party Relationships: Conduct thorough audits of third-party sender relationships to ensure compliance with the new risk management requirements.

By proactively addressing these changes, originators and merchants can mitigate risks, ensure compliance, and continue to facilitate secure and efficient ACH transactions.

June 4, 2024

About Adam Garrett

He has spent almost 20 years building successful merchant acquiring programs and is a proven sales leader who brings his expertise in team management, business development, and strategic planning to Viking Payments. He received his MBA from the University of Texas at Dallas, and his BS at Missouri State University.

Bigger Possibilities Await.

Contact Us


Read More

Demystifying Payment Processing: A Comprehensive Guide

Demystifying Payment Processing

A Comprehensive Guide

In today’s digital world, the process of making payments has evolved significantly. Payment processing is a complex yet essential aspect of modern commerce, enabling seamless transactions between buyers and sellers. Whether you’re buying groceries, booking a flight, or shopping online, understanding how payment processing works is crucial. In this article, we will demystify the intricacies of payment processing, shedding light on the various steps involved in facilitating secure and efficient transactions.

Step 1: Initiating the Transaction

The payment process begins when a customer initiates a purchase by providing their payment information, such as credit card details, debit card numbers, or other digital payment methods. This data is encrypted to protect it from unauthorized access during transmission.

Step 2: Authorization Request

Once the payment information is entered, the merchant or seller sends an authorization request to the payment gateway. The payment gateway acts as an intermediary between the merchant’s point of sale system and the payment processor. It securely transmits the customer’s payment data to the payment processor for further authentication.

Step 3: Authentication and Verification

The payment processor receives the authorization request and forwards it to the customer’s bank (issuing bank) for authentication. The issuing bank verifies the customer’s account details, checks for sufficient funds, and assesses the risk associated with the transaction. If the transaction is approved, the issuing bank sends an authorization code back to the payment processor via the payment gateway.

Step 4: Transaction Settlement

With the authorization code in hand, the payment processor notifies the merchant’s point of sale system about the successful transaction. At this stage, the payment is not yet transferred to the merchant’s bank account.

Step 5: Clearing and Settlement

Once a day, the payment processor batches together all authorized transactions and sends them to the acquiring bank (merchant’s bank) for clearing and settlement. During clearing, the funds are transferred from the customer’s bank to the acquiring bank. The settlement process involves the actual transfer of funds from the acquiring bank to the merchant’s bank account.

Step 6: Payment Reconciliation

After the settlement is complete, the acquiring bank sends the payment data to the payment processor for reconciliation. The processor ensures that all transactions are accurately accounted for and calculates the fees to be deducted for their services.

Step 7: Merchant Receives Funds

Finally, the merchant’s bank account is credited with the settled funds, completing the payment processing cycle. The merchant can then access the funds and utilize them for business purposes.

Security Measures in Payment Processing

Throughout the payment processing journey, various security measures are employed to safeguard sensitive customer information and prevent fraudulent activities. Encryption, tokenization, and secure socket layer (SSL) protocols are utilized during data transmission to protect against unauthorized access. Additionally, the Payment Card Industry Data Security Standard (PCI DSS) sets rigorous guidelines for handling payment information, ensuring the highest level of security compliance.

Conclusion

Payment processing is a sophisticated ecosystem that allows businesses to accept payments seamlessly and customers to shop conveniently. From the moment a customer initiates a transaction to the settlement of funds into the merchant’s account, multiple parties collaborate to make the process smooth, secure, and efficient. Understanding how payment processing works is essential for both businesses and consumers, as it fosters trust and transparency in the digital marketplace. As technology continues to advance, payment processing will undoubtedly evolve, enabling even more seamless and secure transactions in the future.

March 23, 2023

About Adam Garrett

He has spent almost 20 years building successful merchant acquiring programs and is a proven sales leader who brings his expertise in team management, business development, and strategic planning to Viking Payments. He received his MBA from the University of Texas at Dallas, and his BS at Missouri State University.

Bigger Possibilities Await.

Contact Us


Read More